Feature
A certificate that does not rot
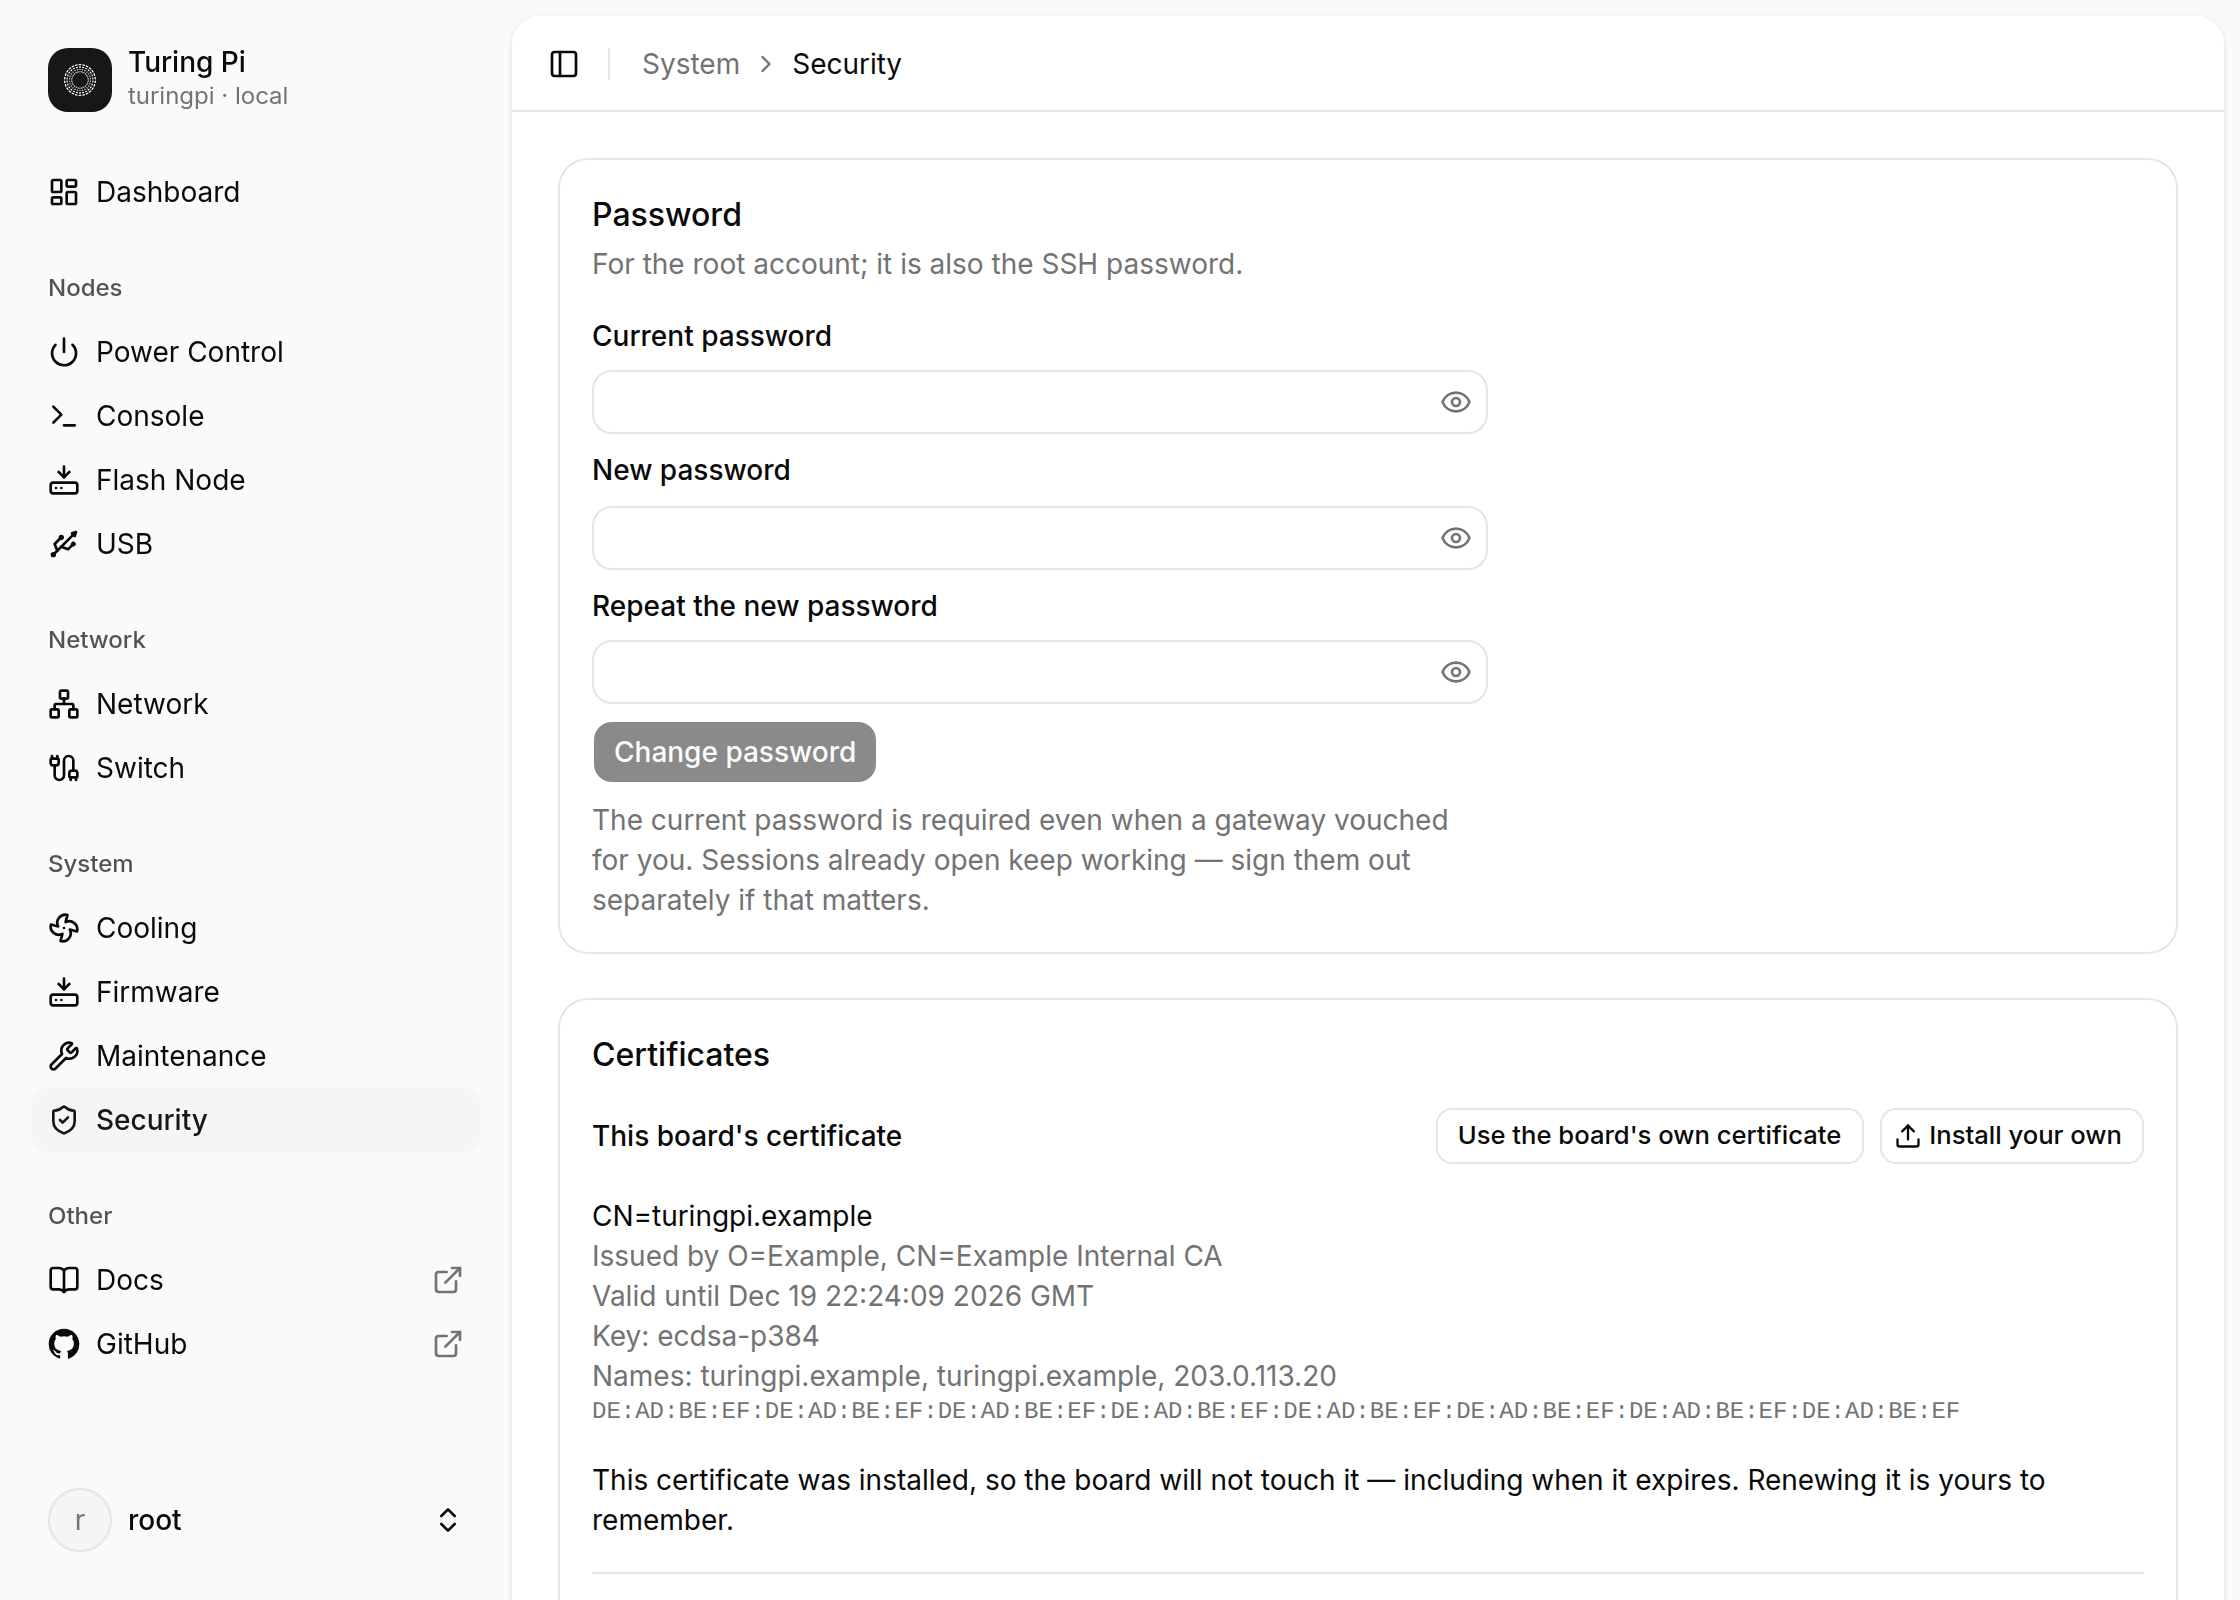
in this fork since v2.23.0Stock firmware serves a certificate no browser will accept, valid for thirty days, and never replaces it. This one is named after the board, renews itself, and will not overwrite yours.
825days of validity, renewed 30 days before it ends
5key types served, each proved by a real handshake
0certificates it will overwrite that it did not issue
the daemon's certificate path, with a real handshake per key type, 2026-09-12.
The argument
Section titled “The argument”An expired self-signed certificate teaches operators to click through warnings, which is the habit that makes every later certificate meaningless. This one carries the board's real names, renews itself 30 days out, and refuses to replace a certificate it did not issue -- so installing your own is safe.